
The new risk in software development

Exploits now outrun patches.
Attackers weaponize new vulnerabilities faster than most teams can remediate them, and legacy AppSec was never built for that gap.

AI code outpaces manual review.
Coding tools like Cursor, Copilot, and Claude Code generate more code than security teams can realistically review by hand.

Every fix needs to teach the system.
One-off remediation doesn't scale. Without context feeding back into how code gets written, teams keep fixing the same class of issue.
Traditional AppSec wasn't built for AI-speed development.
Traditional AppSec
Finds issues after commit
Scores risk by generic CVSS
Fixes issues one at a time
Doesn't learn from past fixes
Agentic

Prevents issues at generation
Prioritizes by exploitability, impact
Remediates in parallel, at scale
Feeds fixes back into AI agents
Meet AgenticAppSec.
Legit brings prevention, context, and autonomous remediation into a single platform, so software teams secure AI-generated code without losing velocity.
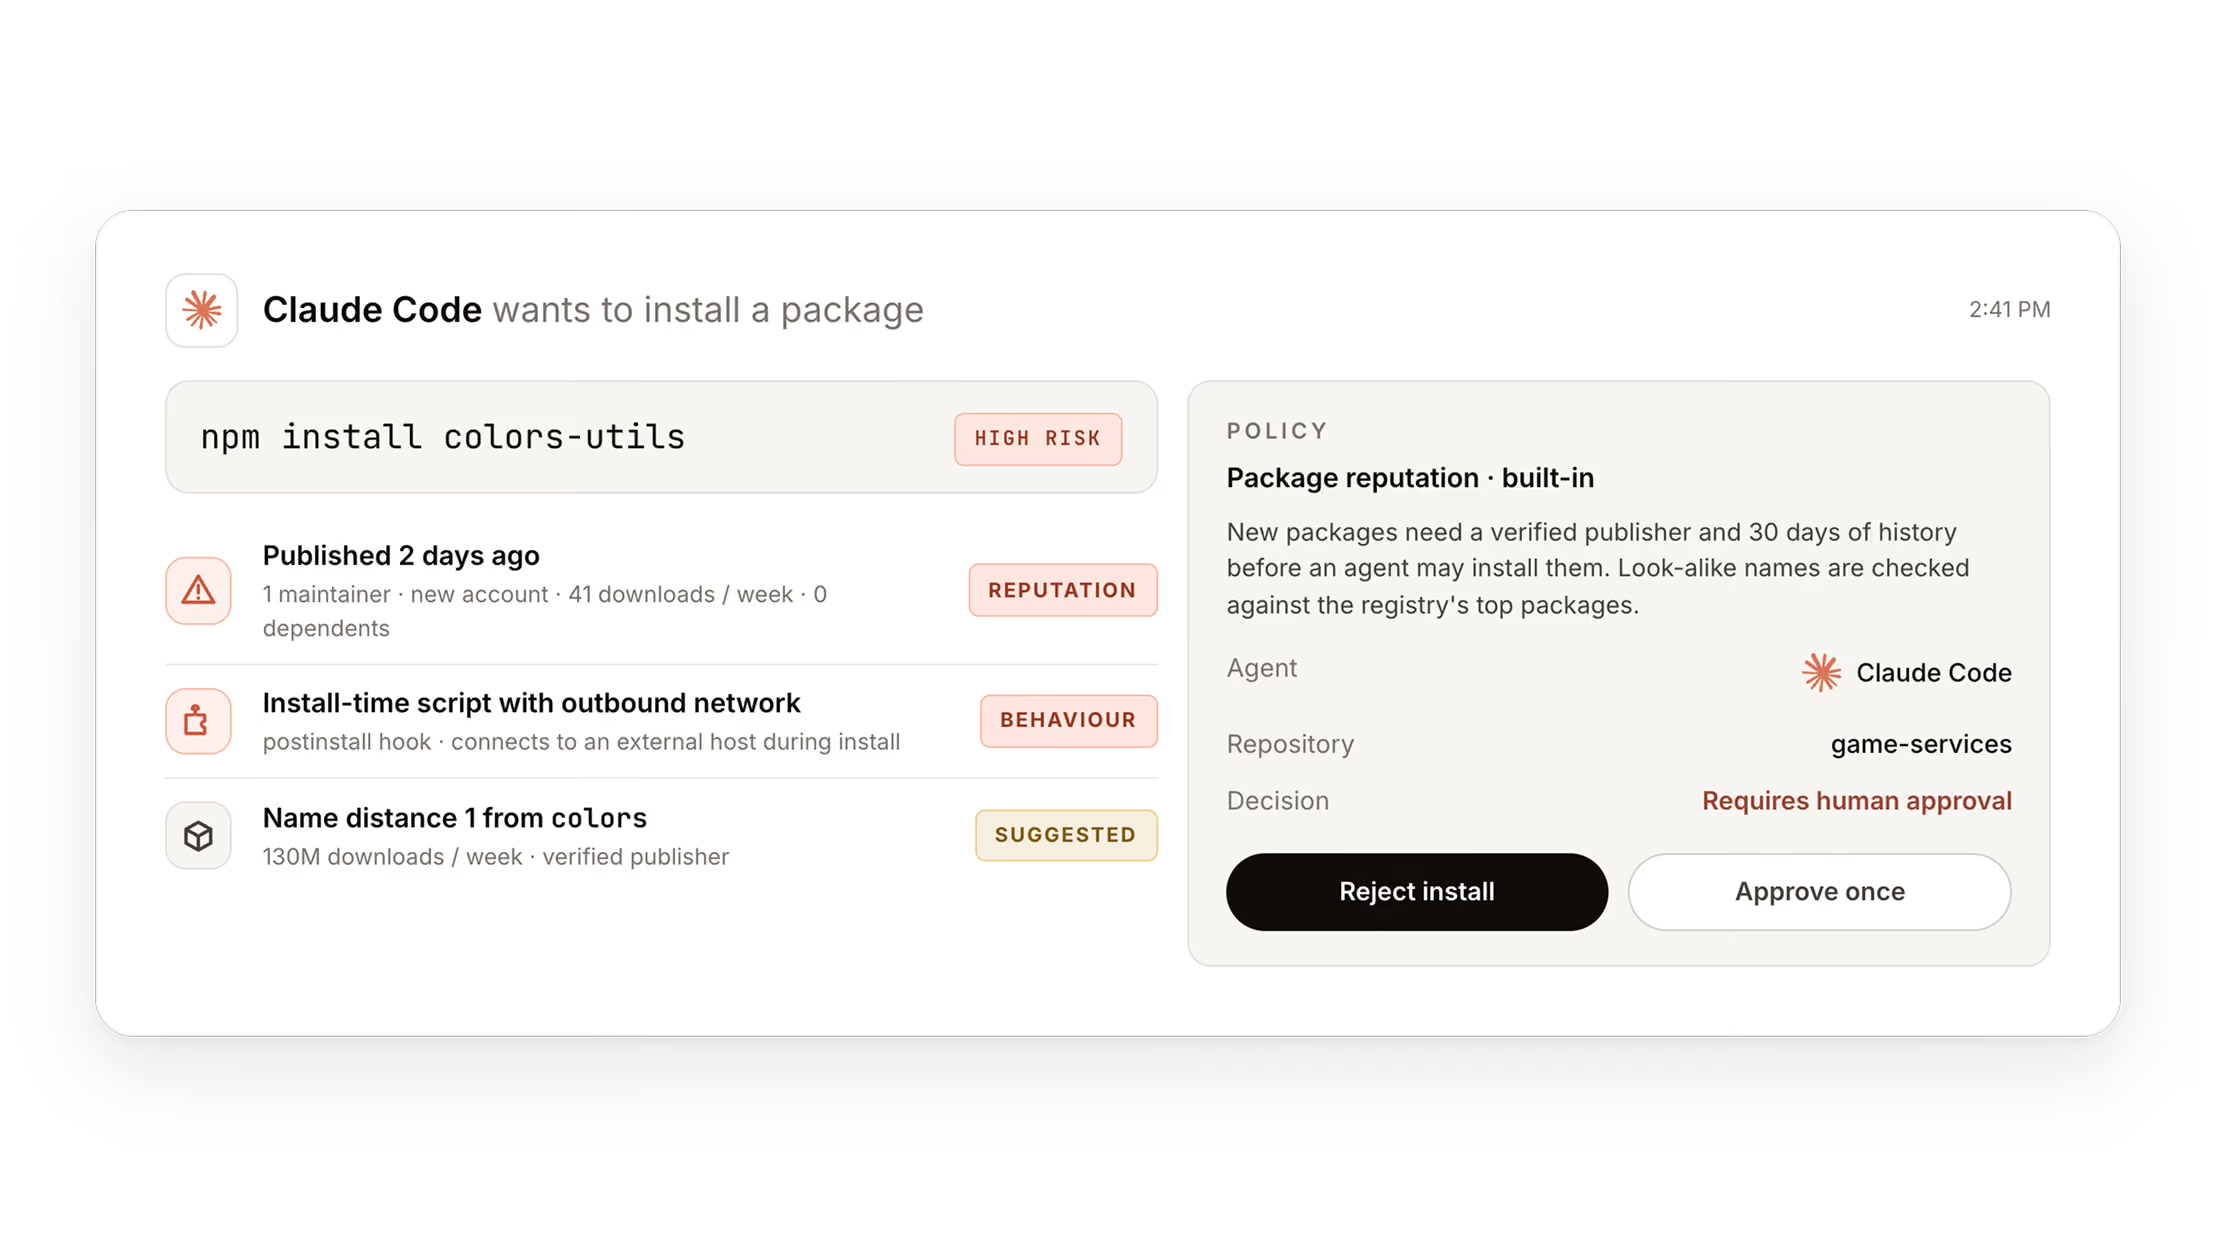
Generate secure code from the first prompt.
Inject threat models and business context directly into Cursor, Copilot, and Claude Code, resolving issues before commit.
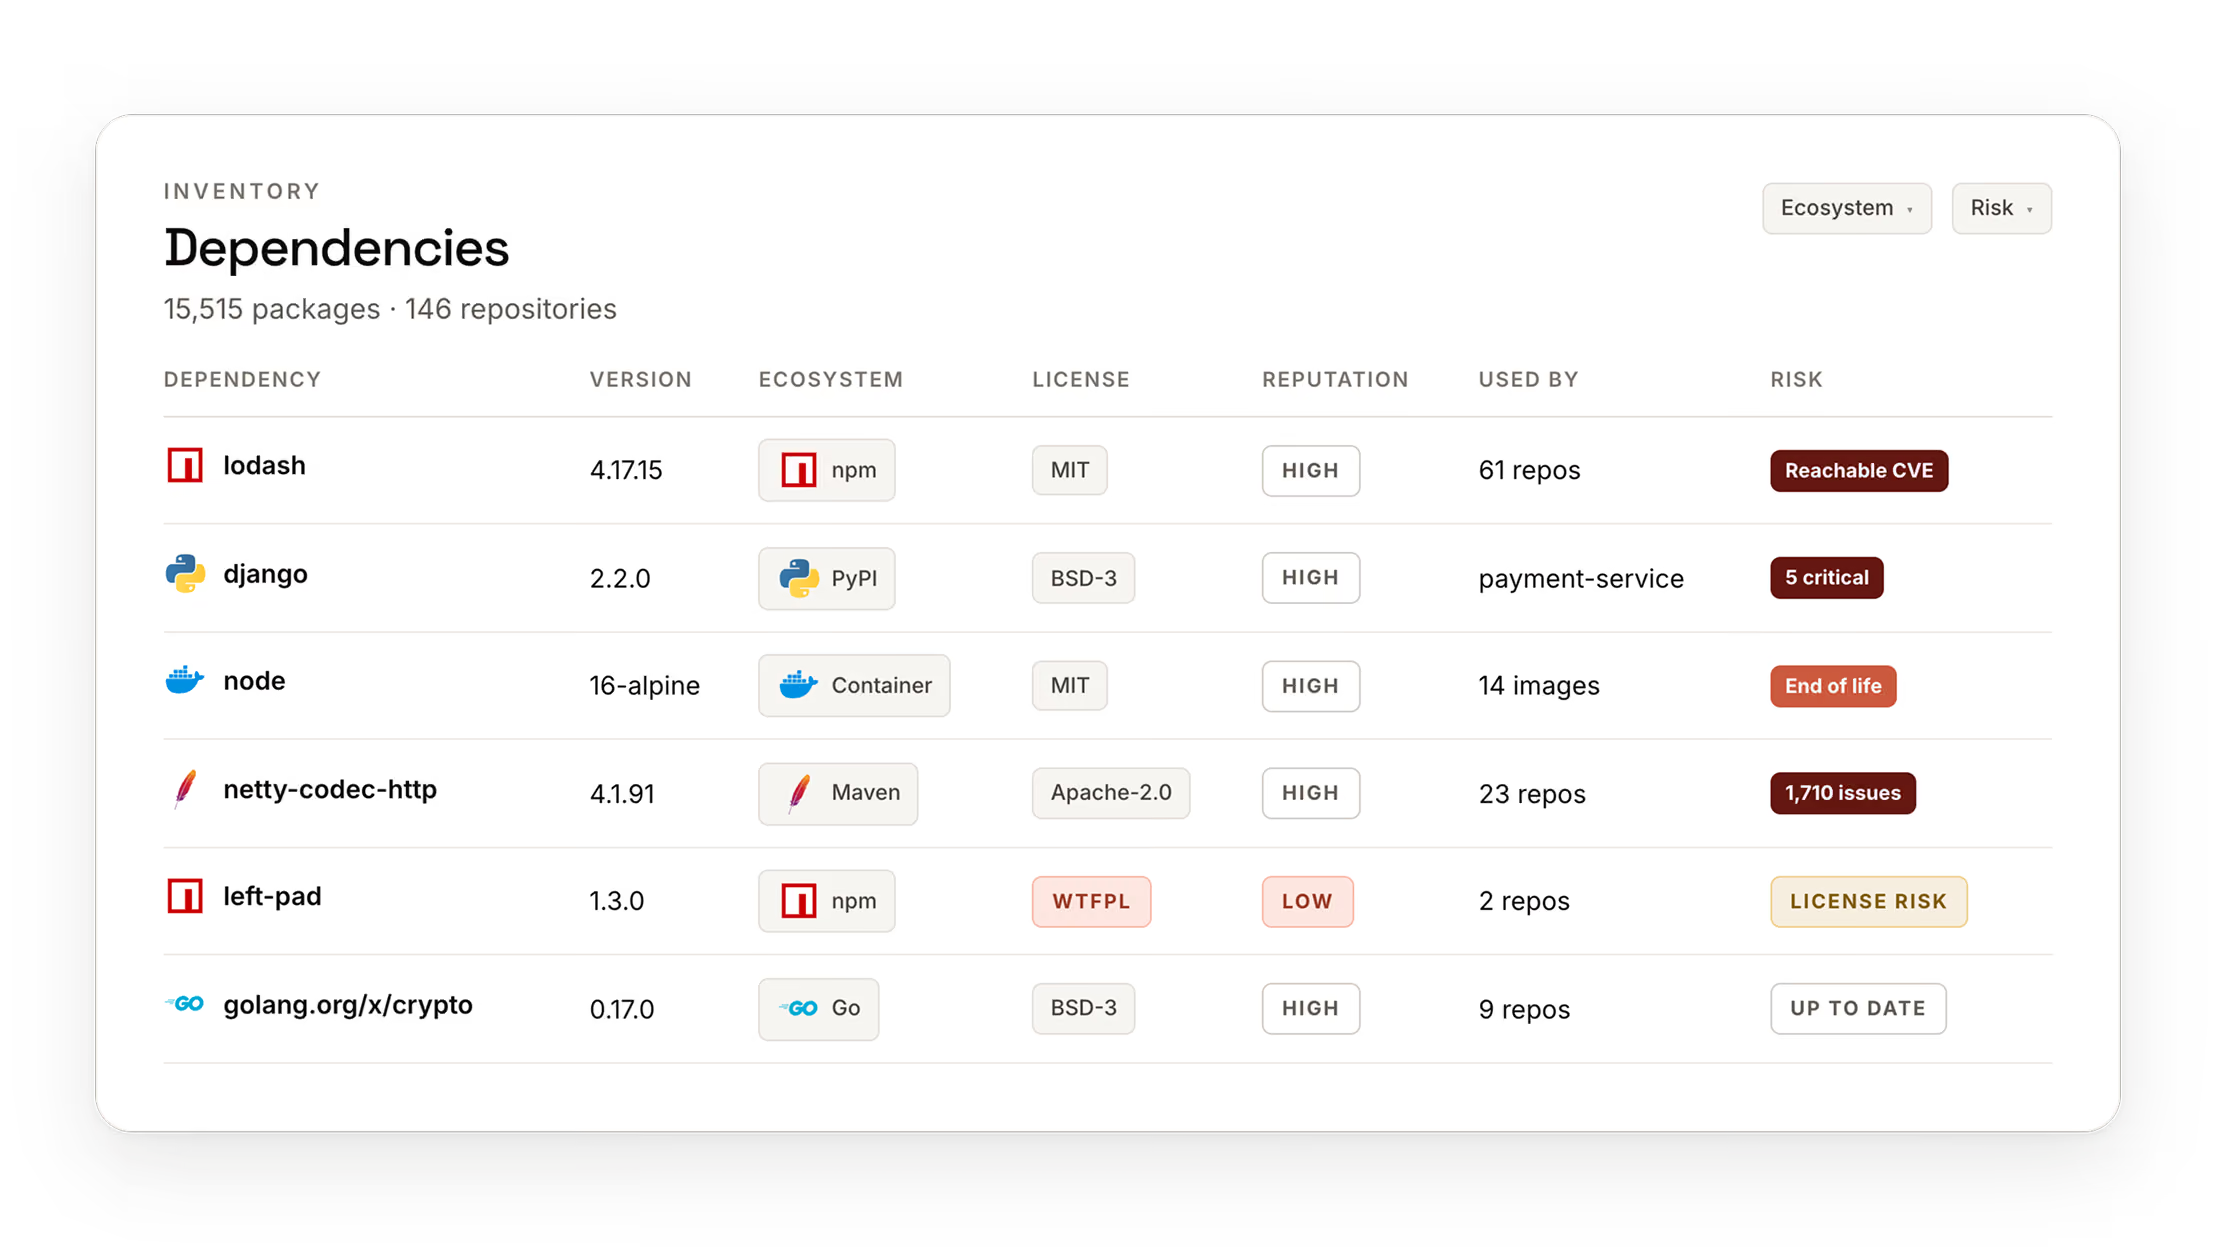
Detect real risk with deep business context.
Score every finding by exposure, reachability, exploitability, EPSS, and CISA KEV status, not generic severity.
Remediate every risk at machine speed.
Agents generate fixes, validate against test suites, and open pull requests in parallel across every affected repository.
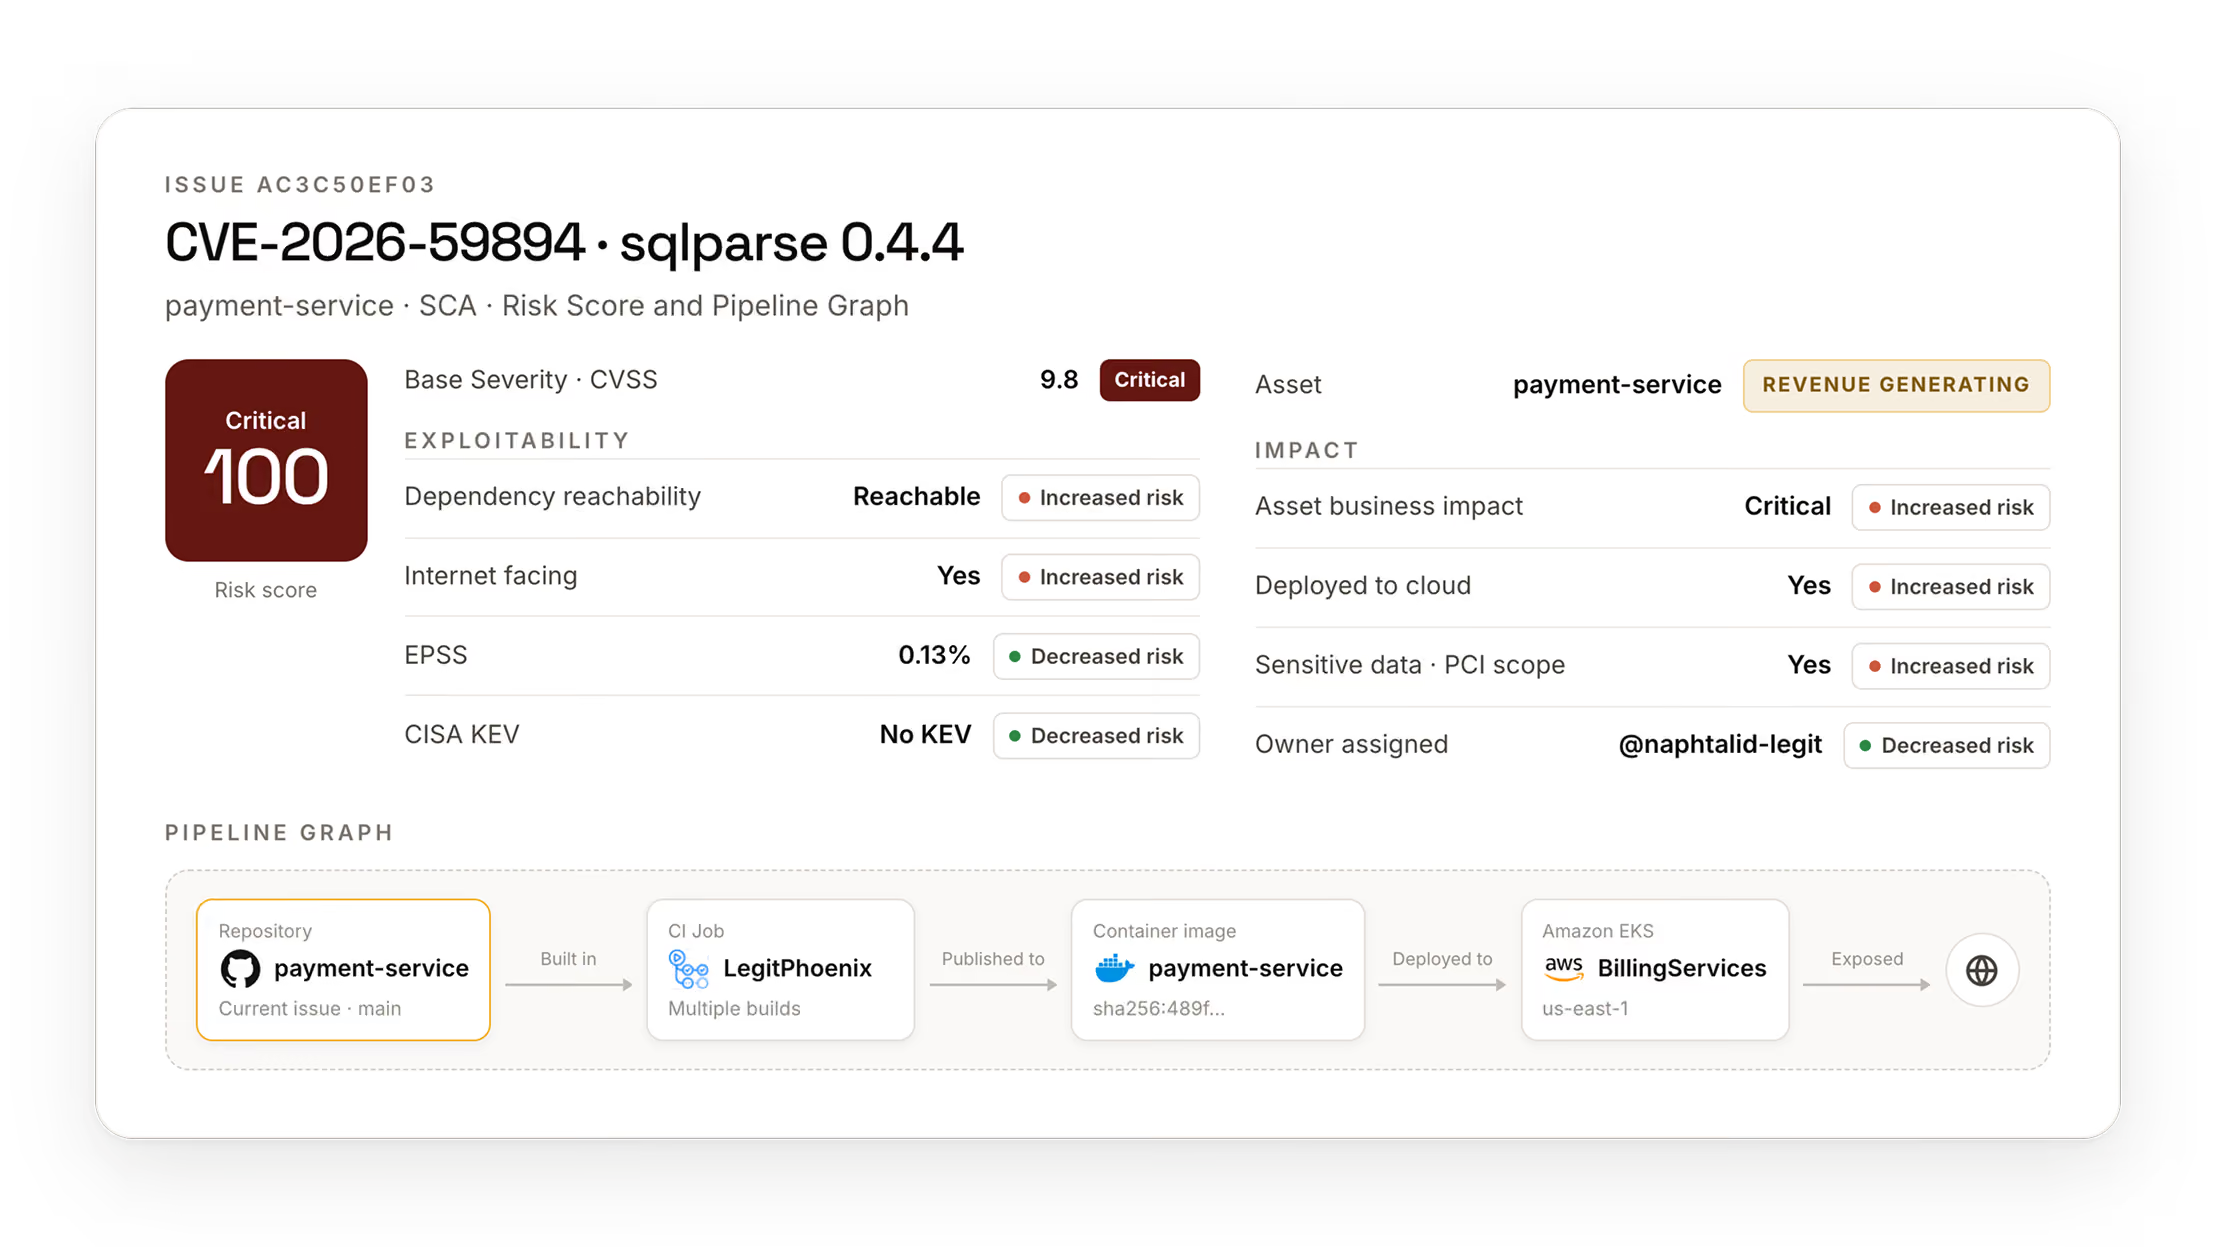
What changes with Legit
Prevent vulnerabilities earlier. Prioritize the risks that matter. Automate remediation.

Every remediation strengthens future AI-generated code, so you create a security program that gets smarter over time.

AI-powered correlation and context reduce total vulnerability noise by more than 90% across every source.

Secrets scanning across code, pipelines, and endpoints cuts false positives by over 95%, closing a common attacker entry point.

"The platform did an outstanding job of correlating the findings from different tools that we use in the organization. Their product has matured a long way since we became their customers, the team has been very supportive and they have really valued our feedback. They have even included us as early adopters of certain features and made customizations that would benefit our organization and their other customers."

"Legit Security has been a game-changer for our application security and DevSecOps programs. As a financial services organization with complex CI/CD pipelines and multiple dev and engineering teams, we needed a single platform that could unify visibility across repos, build systems, and deployment environments - while providing actionable risk context."
"We've had an excellent experience with Legit Security, it offers great visibility and actionable insights across our pipelines and repositories, making it easier to secure and streamline the development process."
More insights for modern AppSec teams
Why I Joined Legit
We believe that security tools had become very good at identifying problems, but that developers were still left with the hardest part: understanding those findings and turning them into secure code changes.

AppSec in the age of AI-first development
Today we launched a new legitsecurity.com. It completes the brand refresh we started this summer with a new voice and visual identity, and it reflects where we’re taking the company.