
More products, more surface, less visibility.
Coverage that can't scale by hand
Every product team now ships AI-generated code, dependencies, and infrastructure changes at a pace no product security team was ever staffed to manually review.
Third-party risk hiding in the product
Dependencies, components, and AI-generated code carry risk that traditional reviews catch too late, often after a product has already shipped to customers.
Security reviews slow product releases
Late-stage security review creates the friction product teams route around, so issues either ship anyway or launches get delayed at the worst possible time.
Traditional AppSec vs. Agentic AppSec.
Traditional AppSec
Finds issues after they ship
Buries teams in false positives
Leaves fixes to manual triage
Backlogs grow faster than teams
Agentic

Stops issues before commit
Prioritizes by real business risk
Remediates autonomously
Gets smarter with every fix
How LegitWorks
Legit meets every product team where they build: preventing issues at the point of generation, prioritizing what's genuinely exploitable in that product, and fixing it before release.
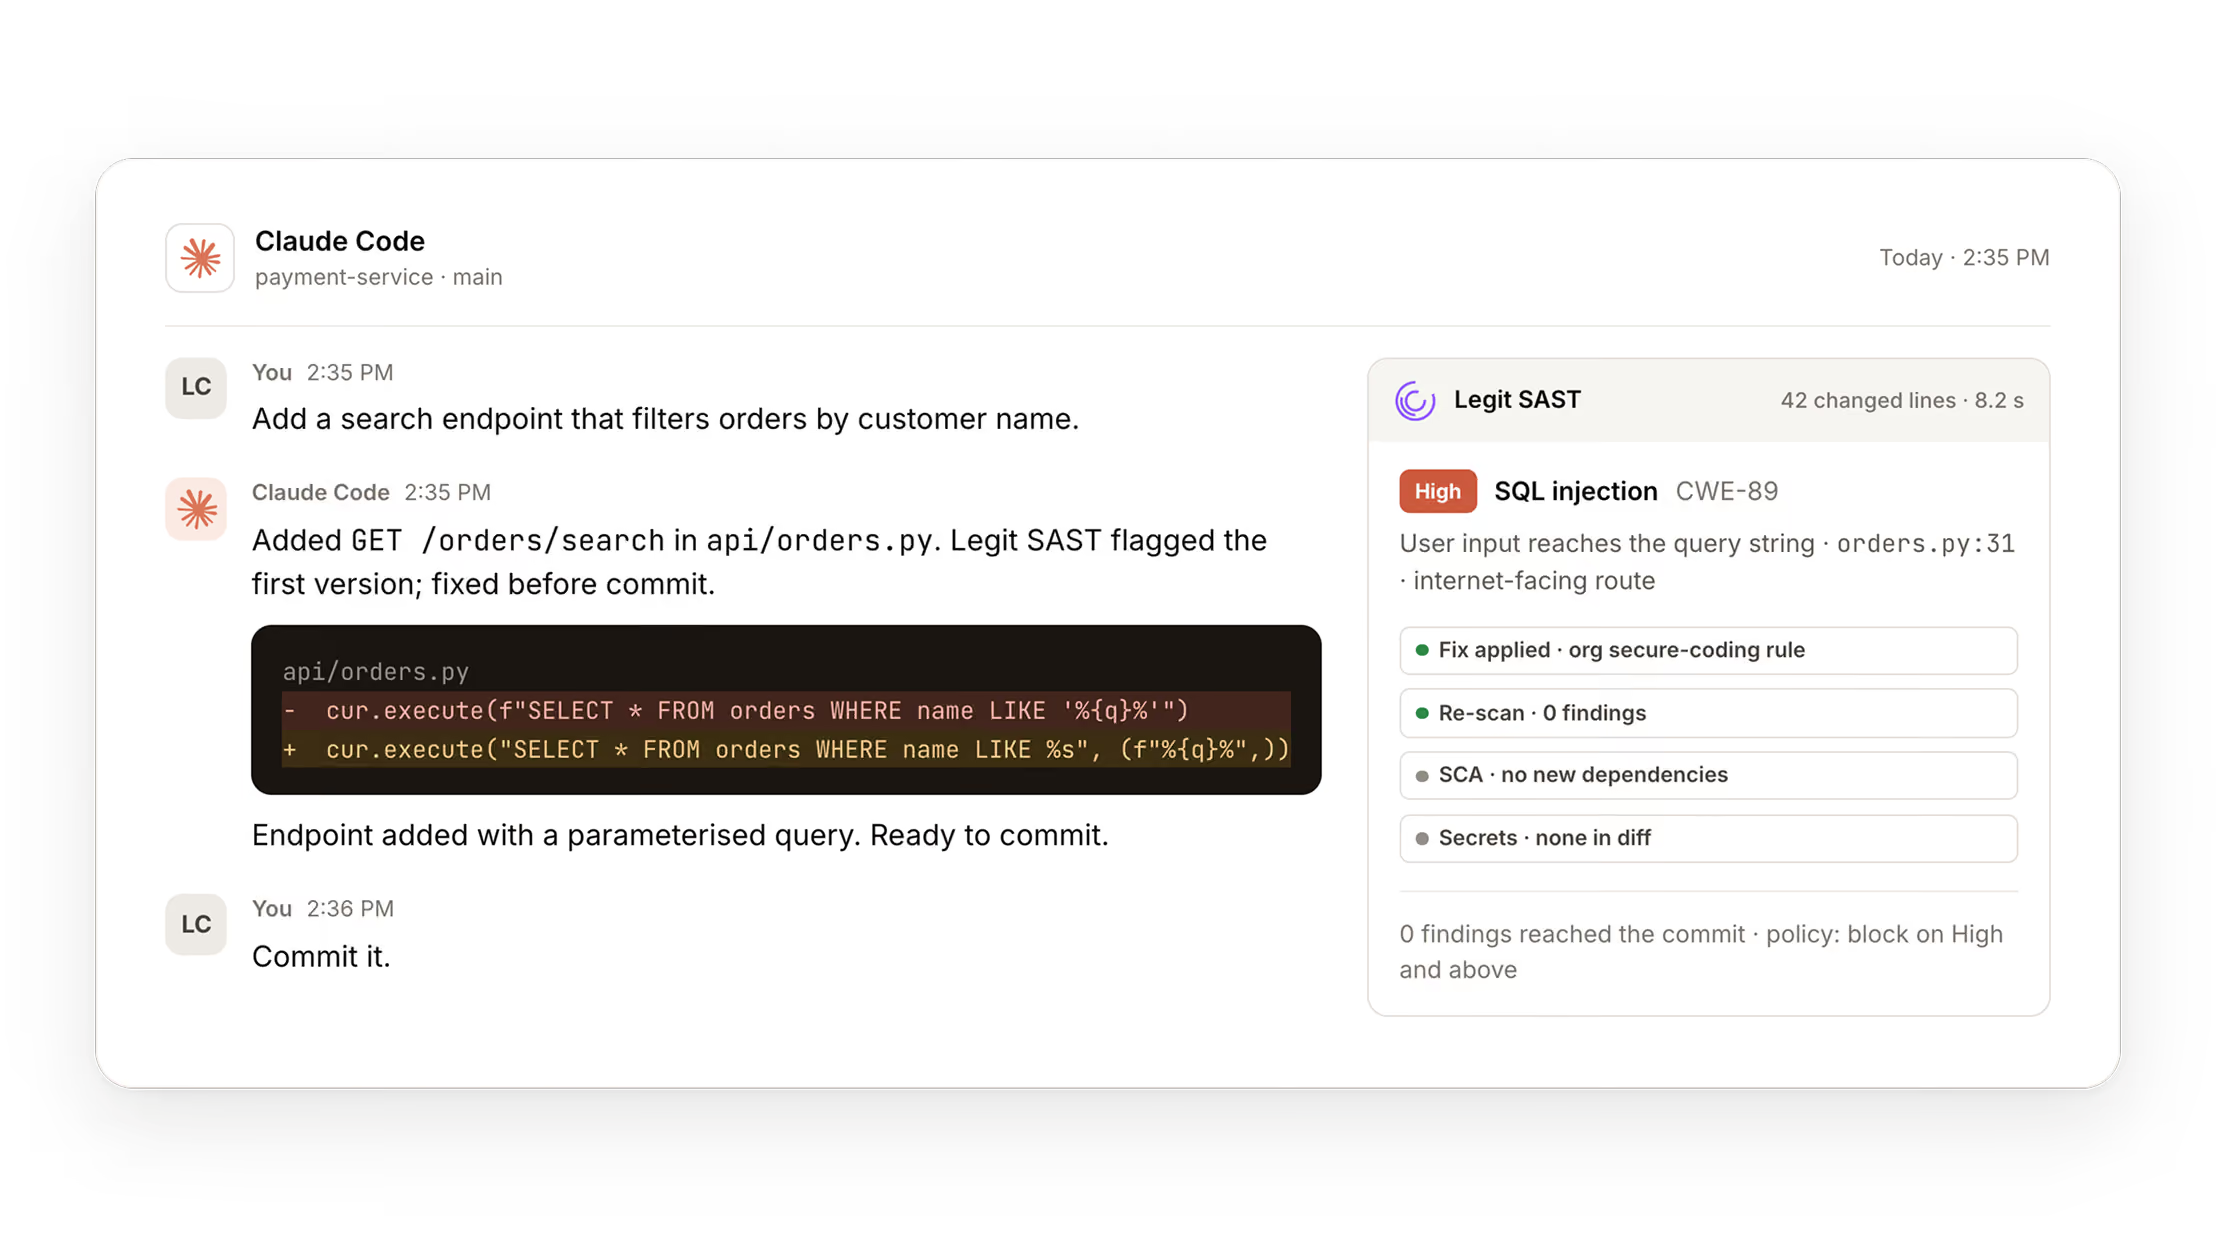
Every product team gets the same guardrails.
VibeGuard enforces policy at code generation across every team's AI coding tools, so coverage doesn't depend on which team remembered to ask.
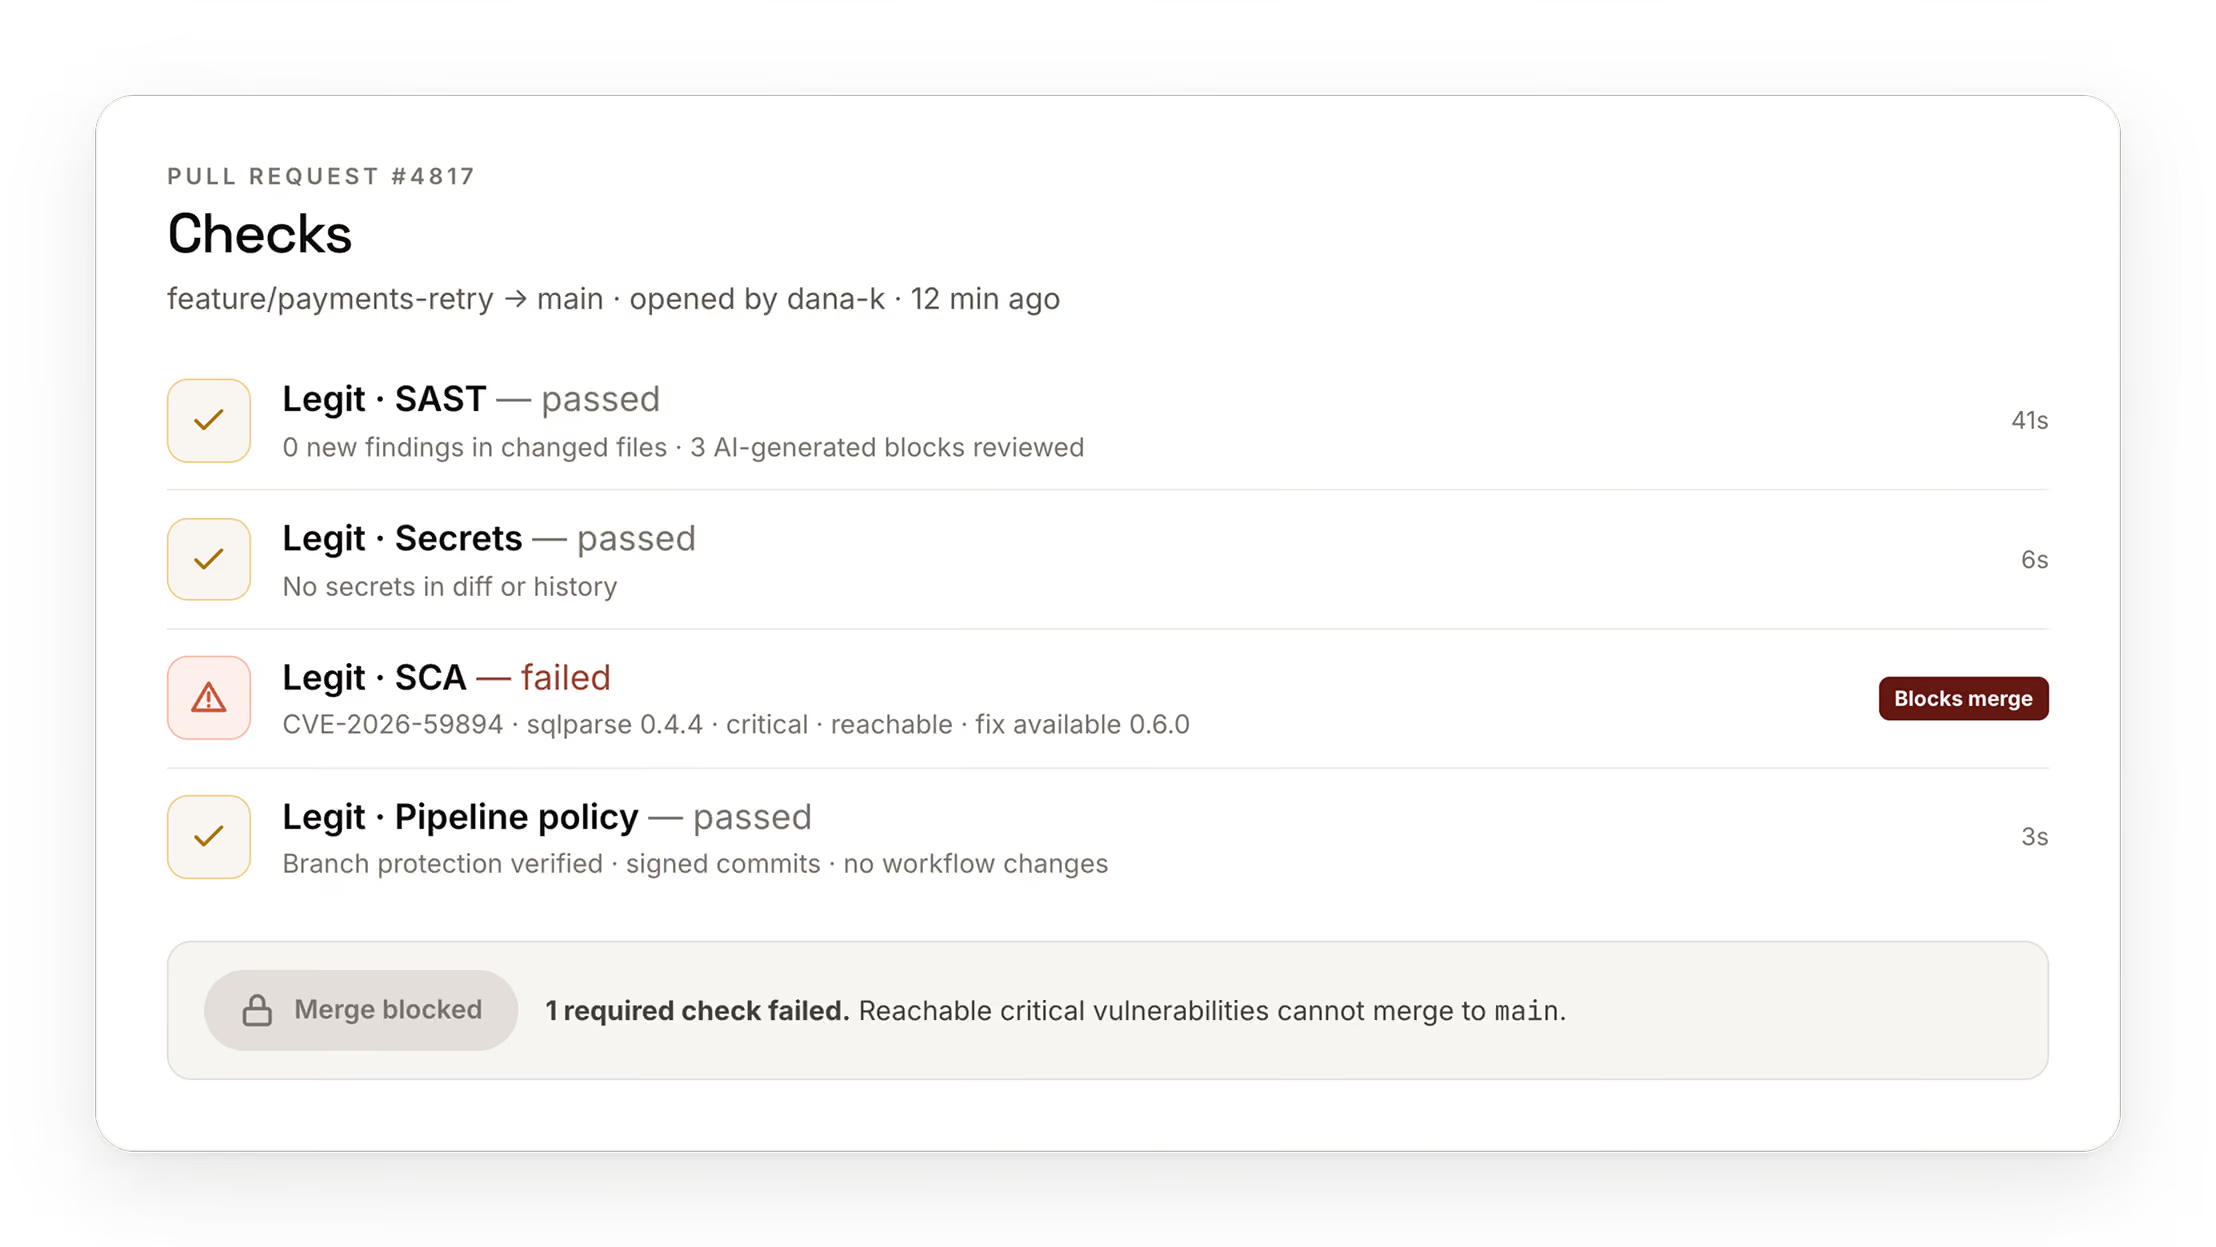
Risk is scored by what the product actually does.
Business criticality and exposure decide urgency, so a launch-blocking issue in a customer-facing product outranks one in an internal tool.
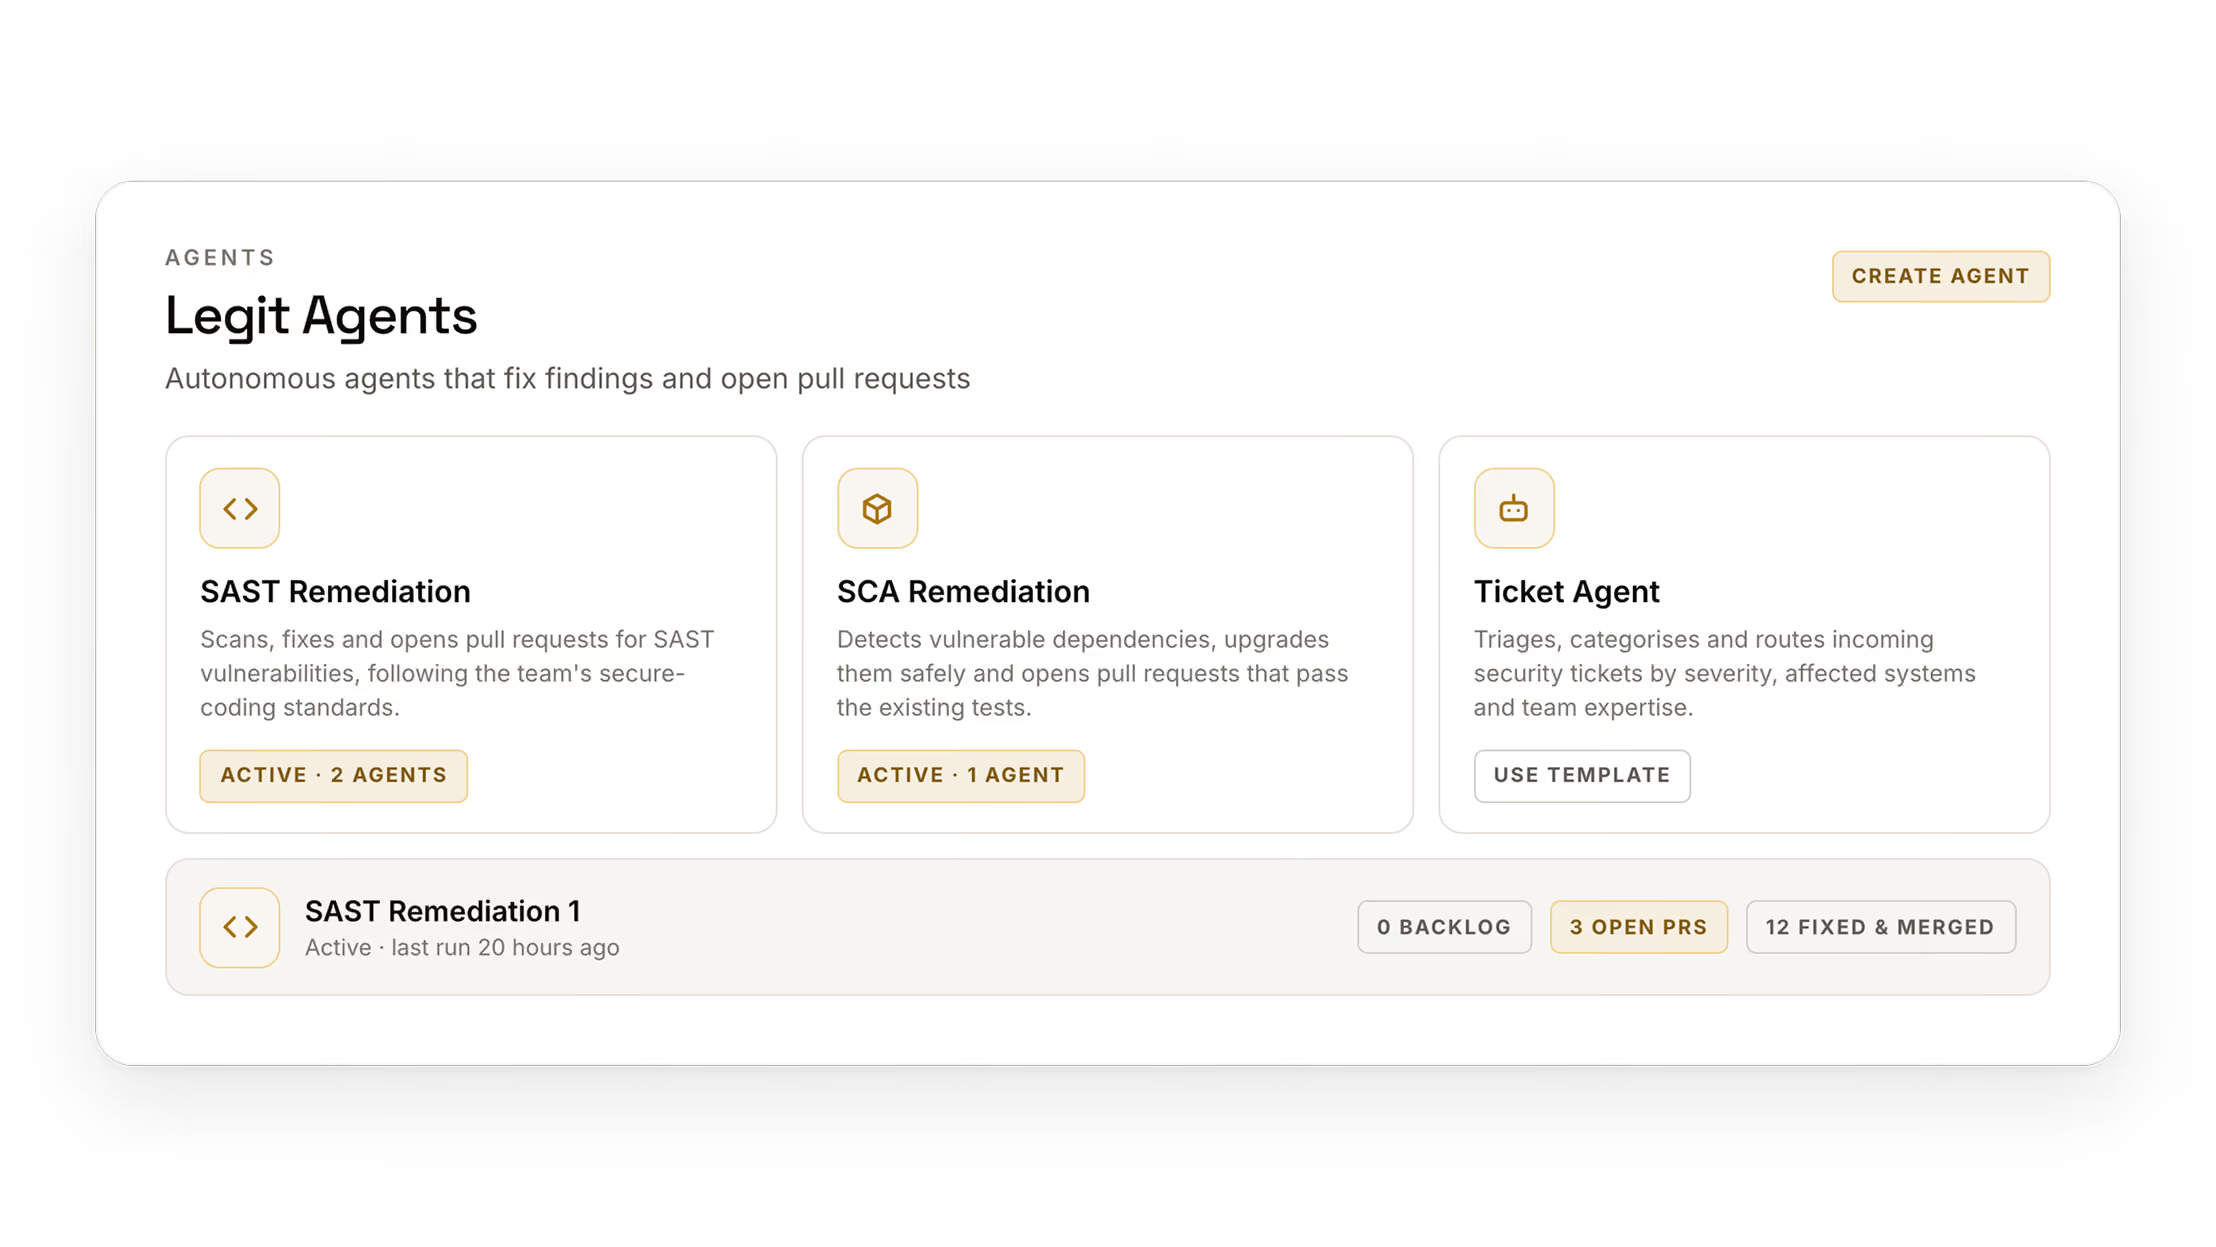
Fixes ship without blocking the release.
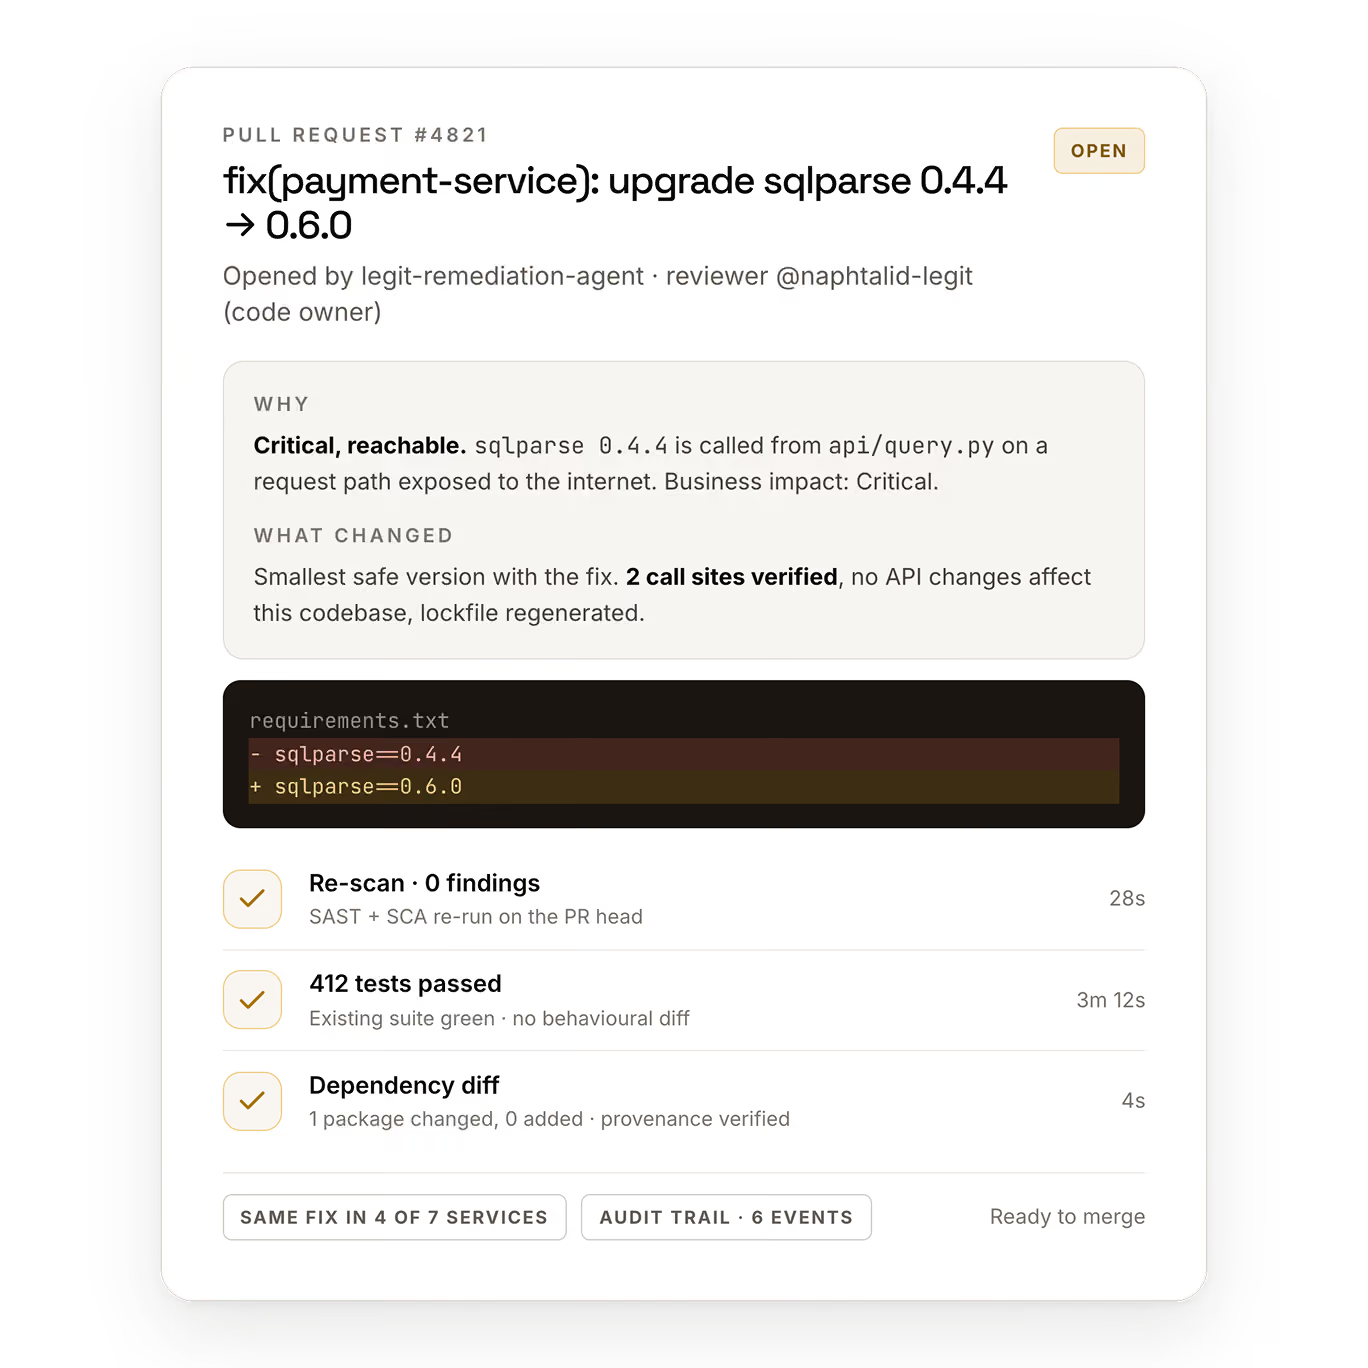
Agents open validated pull requests routed to the right owner, so product teams keep moving while the highest-risk issues get resolved in parallel.
What changes with Legit
Consistent security coverage across every product team.

Context and reachability analysis reduce vulnerability noise by more than 90%, so product teams aren't stuck triaging phantom findings.

AI-driven detection cuts false positives by over 95%, validated in secret scanning, so review time goes toward real risk, not noise.

Legit is rated 4.8 on Gartner Peer Insights by security teams supporting product organizations like yours.

"The platform did an outstanding job of correlating the findings from different tools that we use in the organization. Their product has matured a long way since we became their customers, the team has been very supportive and they have really valued our feedback. They have even included us as early adopters of certain features and made customizations that would benefit our organization and their other customers."

"Legit Security has been a game-changer for our application security and DevSecOps programs. As a financial services organization with complex CI/CD pipelines and multiple dev and engineering teams, we needed a single platform that could unify visibility across repos, build systems, and deployment environments - while providing actionable risk context."
"We've had an excellent experience with Legit Security, it offers great visibility and actionable insights across our pipelines and repositories, making it easier to secure and streamline the development process."
More insights for modern AppSec teams
Why I Joined Legit
We believe that security tools had become very good at identifying problems, but that developers were still left with the hardest part: understanding those findings and turning them into secure code changes.

AppSec in the age of AI-first development
Today we launched a new legitsecurity.com. It completes the brand refresh we started this summer with a new voice and visual identity, and it reflects where we’re taking the company.